Saskia Teichmann
FeedbackPilot
Kostenloses WordPress-Plugin für nachvollziehbare Bug-Reports: Besucher:innen markieren die Stelle im Screenshot; FeedbackPilot erstellt daraus ein GitHub-Issue mit Browser- und Serverkontext.
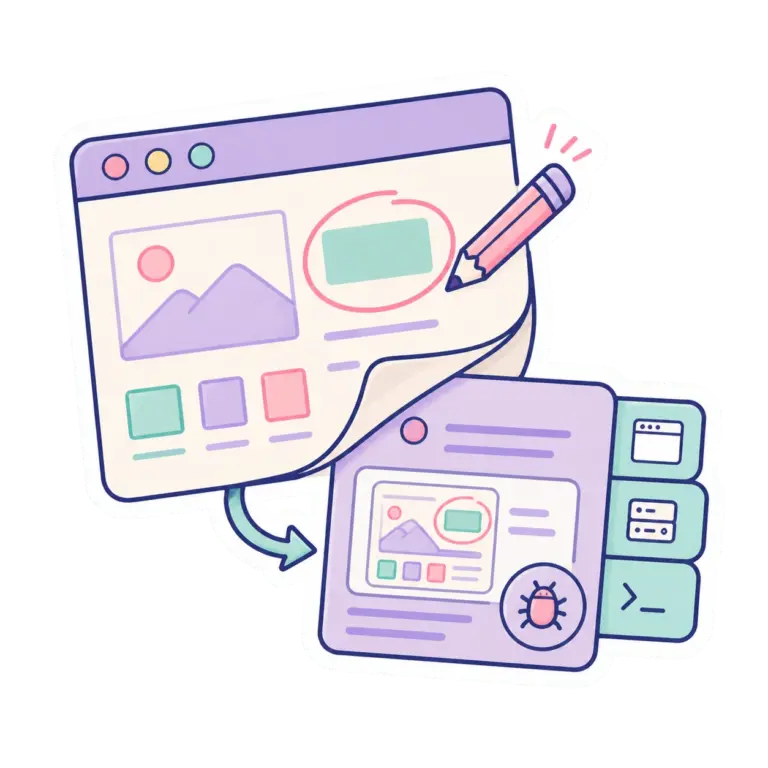
FeedbackPilot ist das WordPress-Plugin, das Bug-Reports deiner Besucher direkt zu Issues in deinem GitHub-Repository macht — mit einem annotierten Screenshot, der Seiten-URL, dem Browser- und Server-Kontext und den letzten Konsolen-Einträgen im Anhang. Du triagierst in GitHub wie gewohnt; deine Besucher klicken nur einen kleinen Button am Bildschirmrand.
So funktioniert FeedbackPilot — in drei Schritten
- Der Besucher klickt auf einen unaufdringlichen „Problem melden“-Button am Bildschirmrand.
- FeedbackPilot erstellt einen Screenshot der aktuellen Seite. Der Besucher zeichnet darauf, wo es klemmt.
- Kurze Beschreibung dazu, absenden — und Sekunden später taucht ein neues Issue in deinem verbundenen GitHub-Repository auf.
Für wen FeedbackPilot gemacht ist
- Seitenbetreiber:innen, die einen reibungsarmen Bug-Report-Kanal wollen, der nicht in einem E-Mail-Postfach versandet.
- Agenturen, die Kundenseiten betreuen und ihren Entwicklern echten Reproduktions-Kontext direkt im Issue-Tracker zeigen wollen.
- Produktteams, die WordPress als Frontend einer größeren Anwendung einsetzen und ihre Engineering-Arbeit ohnehin über GitHub steuern.
Was im GitHub-Issue landet
- Titel: „[Bug] erste 60 Zeichen der Beschreibung…” (oder „[Feedback]” bei Vorschlägen).
- Beschreibung der Nutzer:in, zitiert.
- Annotierter Screenshot als eingebettetes PNG.
- Browser-Kontext: User-Agent, Viewport, Sprache, Plattform, Pixel-Ratio, hell/dunkel.
- Server-Kontext: WordPress-Version, PHP-Version, aktives Theme, Liste der aktiven Plugins, Locale.
- Konsolen-Log: die letzten 200 Einträge (eingeklappt in einem
details-Block). - Labels:
bug,feedbackpilot.
Was bewusst nicht übertragen wird
- Keine Cookies, kein localStorage, keine Formular-Inhalte.
- Keine IP-Adressen, kein Tracking, keine Analytics-Pixel.
- Keine Inhalte aus anderen Browser-Tabs oder Fenstern.
- Keine Tokens, keine Secrets, keine Admin-only-Daten.
Warum nicht ein weiteres SaaS-Tool?
Bug-Reports von Besuchern sind ein Engineering-Input. Sie gehören in denselben Posteingang wie Branch-Reviews, Deploys und Roadmap-Planung — und der heißt für die meisten Teams: GitHub. Tools wie Marker.io, Userback oder Usersnap leisten Ähnliches, sind aber externe Dienste mit eigener Inbox, eigenem Abo und eigener Datenhaltung. FeedbackPilot bleibt in den Werkzeugen, die du ohnehin schon nutzt: WordPress vorne, GitHub hinten, keine neuen Verträge, kein zusätzliches Tracking-Skript auf deiner Seite. Der Code ist Open Source unter der GPL-2.0 — du kannst ihn lesen, anpassen, selbst hosten.
Verbindung zu GitHub — in zwei Klicks
Nach der Installation öffnest du Einstellungen → FeedbackPilot und klickst Connect to GitHub. Du wirst zu github.com geleitet, autorisierst die FeedbackPilot-App, und landest zurück im WordPress-Admin — mit einem verschlüsselt gespeicherten Token. Anschließend trägst du das Ziel-Repository (Format owner/repo) ein und wählst die Besucher-Rollen, die das Widget sehen sollen. Fertig.
Wer den OAuth-Flow nicht nutzen kann oder will, paste alternativ einen Fine-grained Personal Access Token mit „Issues: Read & Write”-Berechtigung auf dem Ziel-Repository ein. Beide Wege funktionieren gleichwertig.
Was du brauchst
- WordPress 6.0 oder neuer.
- PHP 7.4 oder neuer (PHP 8.0 und höher empfohlen).
- Ein GitHub-Account mit einem Repository, in dem du Issues anlegen darfst — der kostenlose GitHub-Tarif reicht aus.
Installation in unter zwei Minuten
- ZIP-Datei nach dem Download über Plugins → Installieren → Plugin hochladen einspielen.
- Aktivieren.
- Unter Einstellungen → FeedbackPilot mit GitHub verbinden und das Ziel-Repository wählen.
- Lizenzschlüssel eintragen — damit das Plugin sich künftig automatisch aktualisiert.
Häufige Fragen
Brauche ich einen kostenpflichtigen GitHub-Tarif?
Nein. Auch kostenlose GitHub-Accounts können in eigenen Repositories Issues anlegen. Das Plugin funktioniert in beiden Welten identisch.
Funktioniert es mit privaten Repositories?
Ja. Der OAuth-Flow autorisiert die FeedbackPilot-App auf den Repos, die du auswählst — private inklusive. Der manuelle PAT-Weg funktioniert analog.
Verlangsamt das Widget meine Seite?
Nein. Die einzige externe Bibliothek (html2canvas) wird erst geladen, wenn ein Besucher tatsächlich auf den Button klickt. Bis dahin sind nur ein kleines CSS-File und ein leichtes JavaScript-File aktiv. Die Auswirkung auf Page Speed und Core Web Vitals ist vernachlässigbar.
Funktioniert es mit Caching-Plugins, Cloudflare oder WP Rocket?
Ja. Die Widget-Skripte sind statisch und werden problemlos gecached. Konfigurationsänderungen werden beim Seitenaufbau gelesen und brauchen keinen Cache-Reset.
Kann ich Reports an etwas anderes als GitHub schicken?
In der aktuellen Version 0.1.x ist GitHub das einzige Ziel. Wenn dich E-Mail-Versand, Slack oder Linear-Tickets unblocken würden, freuen wir uns über deinen Vorschlag im GitHub-Repository.
Wo bleibt der Screenshot?
Auf deiner WordPress-Seite unter wp-content/uploads/feedbackpilot/. Das GitHub-Issue verlinkt das Bild von dort. Es wird nicht zu einem Drittanbieter hochgeladen.
Lizenz, Updates und Support
FeedbackPilot ist freie Software unter der GPL-2.0-or-later — derselben Lizenz wie WordPress selbst. Der Download auf dieser Seite ist und bleibt kostenfrei. Mit dem mitgelieferten Lizenzschlüssel erhältst du automatische Updates über den ganz normalen WordPress-Update-Mechanismus. Den vollständigen Quellcode findest du auf GitHub. Fragen, Bug-Reports und Feature-Wünsche gerne über das Repository oder per Mail an hello@isla-stud.io.
Änderungsprotokoll
1.1.6
- Prevents stacked dialogs and duplicate screenshot captures after rapid clicks.
- Announces screenshot preparation and falls back after 7.5 seconds.
- Cleans dialog listeners, timers and spam checks on every close path.
- Keeps the console catcher synchronous without an invalid WordPress script strategy.
1.1.5
- Keeps the cloned viewport at the click-time scroll position when clone-only layout repairs would otherwise trigger browser scroll anchoring.
- Strengthens the cross-browser screenshot gate with a visible downstream anchor and exact vertical landmark comparison.
- Prevents text in tightly padded, fixed-height input fields from being vertically clipped in screenshots.
- Builds the release ZIP from a verified allowlist and checks the bundled browser-asset provenance and checksums before publication.
1.1.4
- Keeps scrolled screenshots aligned on pages that combine smooth scrolling with dynamic float/clearfix layouts.
- Preserves fixed elements, the live scroll position, and the page's original inline scroll styles while cloning.
- Runs the real FeedbackPilot screenshot path in Chromium, Firefox, and WebKit before merge and release.
- Updates vulnerable development-only lint dependencies and aligns optimized Composer autoloading with the plugin's WordPress-style filenames; development tools are not included in the plugin ZIP.
1.1.3
- Captures the viewport the visitor is actually viewing after scrolling, including themes whose document uses visible overflow.
- Lets site owners hide the guidance beside the public button while keeping it visible inside the report form.
- Ships complete German translations for both de_DE and de_DE_formal.
- Verifies new Turnstile credentials before saving and distinguishes visitor challenge failures from configuration or temporary provider failures.
1.1.2
- Lets site owners customize the public widget button and a directly visible guidance notice from Settings -> FeedbackPilot.
- Uses translated privacy-safe defaults when either field is missing, empty, or whitespace-only, with no migration required for existing installations.
- Sanitizes both settings as plain text, repeats the notice inside the form, and adds automated regression coverage.
1.1.1
- Bundles html2canvas-pro and the native Altcha fallback in the plugin ZIP so FeedbackPilot no longer requires visitor-browser requests to jsDelivr.
- Keeps optional Cloudflare Turnstile as an explicit admin-enabled spam-protection integration.
- Updates privacy/GDPR documentation to reflect the local asset delivery model.
1.1.0
- Adds FeedbackPilot support for WordPress login, lost-password, retrieve-password, and reset-password screens.
- Adds sanitized auth-screen context to generated issues so reports from login/reset pages are easy to triage.
- Redacts reset keys, login identifiers, nonces, tokens, and password-like values from auth-screen URLs, console logs, and issue bodies.
- Clears sensitive login/reset form fields from the cloned screenshot document before rendering, without changing the live page.
1.0.5
- Adds a trusted triage gate to generated GitHub issues so maintainers and LLM agents validate visitor reports before turning them into code changes.
- Requires non-implementation outcomes such as already shipped, duplicate, needs more information, not planned, irrelevant, or spam to remain explicit options during triage.
- Updates LLM-agent guidance and smoke checks for this prompt-injection defence-in-depth layer.
1.0.4
- Makes the visitor-facing widget and modal copy easier to understand for non-technical users; GitHub and issue-tracker wording is kept out of the frontend.
- Localizes the native Altcha fallback challenge UI when the standalone Altcha WordPress plugin is not installed.
- Prevents browser/password-manager autofill from interfering with Turnstile credential fields in the settings page.
1.0.3
- Shows friendly, localized submit error messages instead of internal REST error codes such as rate_limited.
1.0.2
- Fixes captcha-protected submissions incorrectly hitting the unauthenticated 60-second burst limiter after a solved Altcha or Turnstile challenge.
- Failed or missing captcha submissions no longer consume a report rate-limit slot; the hourly per-IP cap still applies to successful reports.
1.0.1
- Fixes screenshot capture on pages where CSS text-transform changes text length, avoiding an upstream html2canvas-pro Range.setEnd IndexSizeError.
- Documents Cloudflare Turnstile CSP requirements for sites with strict Content Security Policy headers.
- Adds a reduced browser fixture for the html2canvas text-transform regression.
1.0.0
- First stable release for production use.
- Adds GDPR-readiness improvements: visitor-facing privacy notice, admin controls to disable screenshot capture and console-log inclusion, and server-side enforcement of those minimisation settings.
- Hardens Cloudflare Turnstile validation by binding tokens to the expected action and hostname.
- Keeps the v0.1.16 security hardening: native Altcha replay protection, prompt-injection boundaries, proxy-aware rate limiting, AES-256-GCM token storage, and validated screenshot storage.
- Updates README, German README, readme.txt, wiki privacy guidance, translations, and smoke checks for the v1.0 release.
0.1.16
- Security hardening release: native Altcha fallback now uses delimited salts, strict validation, expiry checks, and replay protection.
- Prompt-injection follow-up: visitor-supplied metadata and console logs are fenced/normalized as untrusted content, with a PII-minimized suspected-injection hook for integrations.
- Rate limits now trust only REMOTE_ADDR by default, with explicit Cloudflare and generic reverse-proxy modes.
- Token storage now uses a versioned AES-256-GCM envelope where available, with legacy AES-256-CBC read/migration support.
- Screenshot storage now enforces PNG dimension/pixel ceilings and re-encodes PNGs via GD when available.
- Turnstile secret placeholders no longer risk overwriting stored secrets; update-cache flushing now targets only FeedbackPilot's EDD-SL cache key.
0.1.0
- Initial release. Console catcher, annotated screenshot, GitHub-Issue submission via OAuth-connected user token (or manual fine-grained PAT).