Saskia Teichmann
FeedbackPilot
Free WordPress plugin for detailed bug reports: Visitors mark the location in a screenshot; FeedbackPilot uses this information to create a GitHub issue that includes browser and server context.
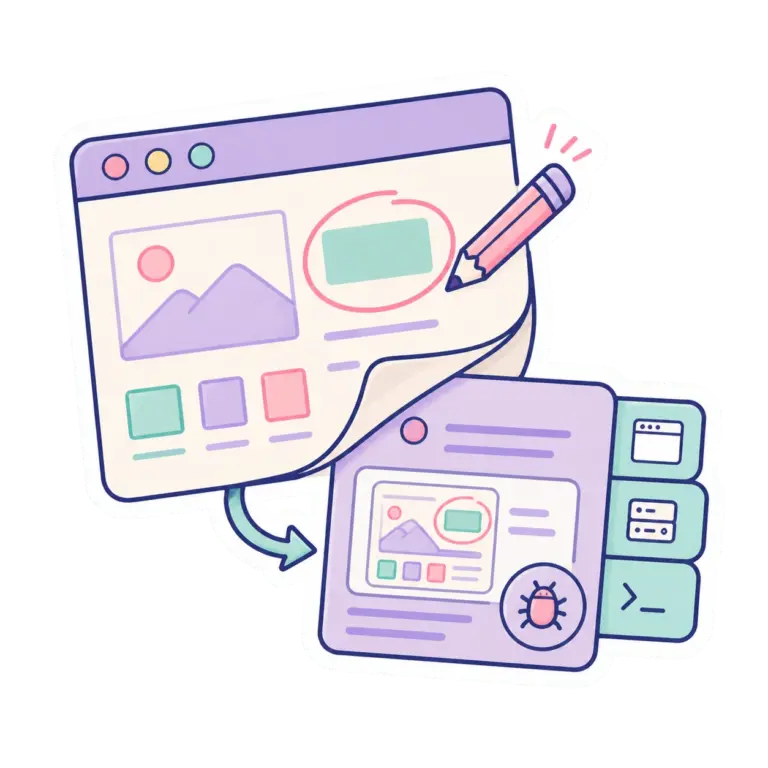
FeedbackPilot is the WordPress plugin that turns your visitors' bug reports directly into issues in your GitHub repository - with an annotated screenshot, the page URL, the browser and server context and the latest console entries attached. You triage in GitHub as usual; your visitors just click a small button on the side of the screen.
How FeedbackPilot works - in three steps
- The visitor clicks on a discreet „Report a Problem“ button at the edge of the screen.
- FeedbackPilot creates a screenshot of the current page. The visitor draws on it where there is a problem.
- Add a short description, submit - and seconds later a new issue will appear in your connected GitHub repository.
Who FeedbackPilot is made for
- Site operator, who want a low-friction bug report channel that doesn't end up in an email inbox.
- Agencies, who maintain customer sites and want to show their developers real reproduction context directly in the issue tracker.
- Product teams, who use WordPress as the front end of a larger application and manage their engineering work via GitHub anyway.
What ends up in the GitHub issue
- Title: „[Bug] First 60 characters of the description...“ (or „[Feedback]“ for suggestions).
- Description of the users:in, cited.
- Annotated screenshot as an embedded PNG.
- Browser context: User agent, viewport, language, platform, pixel ratio, light/dark.
- Server context: WordPress version, PHP version, active theme, list of active plugins, locale.
- Console log: the last 200 entries (collapsed into a
details-Block). - Labels:
bug,feedbackpilot.
What is deliberately not transferred
- No cookies, no localStorage, no form content.
- No IP addresses, no tracking, no analytics pixels.
- No content from other browser tabs or windows.
- No tokens, no secrets, no admin-only data.
Why not another SaaS tool?
Bug reports from visitors are an engineering input. They belong in the same inbox as branch reviews, deploys and roadmap planning - which for most teams is GitHub. Tools such as Marker.io, Userback or Usersnap do similar things, but are external services with their own inbox, subscription and data storage. FeedbackPilot remains in the tools you already use: WordPress up front, GitHub behind, no new contracts, no additional tracking script on your site. The code is open source under the GPL 2.0 - you can read it, adapt it, host it yourself.
Connection to GitHub - in two clicks
After the installation, open Settings → FeedbackPilot and click Connect to GitHub. You will be redirected to github.com, authorize the FeedbackPilot app, and end up back in the WordPress admin - with an encrypted token. You then enter the target repository (format owner/repo) and select the visitor roles that should see the widget. Done.
If you cannot or do not want to use the OAuth flow, you can instead paste a fine-grained personal access token with „Issues: Read & Write“ permissions into the target repository. Both methods work equally well.
What you need
- WordPress 6.0 or newer.
- PHP 7.4 or newer (PHP 8.0 and higher recommended).
- A GitHub account with a repository in which you can create issues - the free GitHub plan is sufficient.
Installation in under two minutes
- ZIP file after download via Plugins → Install → Upload plugin record.
- Activate.
- Under Settings → FeedbackPilot connect to GitHub and select the target repository.
- Enter the license key - so that the plugin updates itself automatically in future.
Frequently asked questions
Do I need a paid GitHub plan?
No. Free GitHub accounts can also create issues in their own repositories. The plugin works identically in both worlds.
Does it work with private repositories?
Yes, the OAuth flow authorizes the FeedbackPilot app on the repos you select - including private ones. The manual PAT path works in the same way.
Does the widget slow down my site?
No. The only external library (html2canvas) is only loaded when a visitor actually clicks on the button. Until then, only a small CSS file and a small JavaScript file are active. The effect on page speed and core web vitals is negligible.
Does it work with caching plugins, Cloudflare or WP Rocket?
Yes, the widget scripts are static and are cached without any problems. Configuration changes are read when the page is loaded and do not require a cache reset.
Can I send reports to something other than GitHub?
In the current version 0.1.x, GitHub is the only target. If sending emails, Slack or linear tickets would unblock you, we would be happy to receive your suggestion in the GitHub repository.
Where is the screenshot?
On your WordPress page under wp-content/uploads/feedbackpilot/. The GitHub image links the image from there. It is not uploaded to a third-party provider.
License, updates and support
FeedbackPilot is free software under the GPL-2.0-or-later - the same license as WordPress itself. The download on this page is and remains free of charge. With the included license key, you will receive automatic updates via the normal WordPress update mechanism. You can find the complete source code on GitHub. Questions, bug reports and feature requests are welcome via the repository or by email to hello@isla-stud.io.
Change Log
1.1.6
- Prevents dialog boxes from piling up and duplicate screenshots from being taken after rapid clicks.
- Announces that a screenshot is being taken and reverts after 7.5 seconds.
- Clears dialog listeners, timers, and spam checks on every close path.
- Keeps the console catcher synchronous without using an invalid WordPress script strategy.
1.1.5
- Keeps the cloned viewport at the scroll position at the time of the click when "clone-only" layout repairs would otherwise trigger browser scroll anchoring.
- Strengthens the cross-browser screenshot validation process with a visible downstream anchor and an exact vertical landmark comparison.
- Prevents text in tightly spaced, fixed-height input fields from being vertically cropped in screenshots.
- Builds the release ZIP from a verified allowlist and verifies the provenance and checksums of the bundled browser assets before publication.
1.1.4
- Keeps scrolled screenshots aligned on pages that combine smooth scrolling with dynamic float/clearfix layouts.
- Preserves fixed elements, the live scroll position, and the page's original inline scroll styles during cloning.
- Runs the actual FeedbackPilot screenshot path in Chromium, Firefox, and WebKit before merging and releasing.
- Updates vulnerable lint dependencies intended for development only and aligns optimized Composer autoloading with the plugin's WordPress-style filenames; development tools are not included in the plugin ZIP file.
1.1.3
- Captures the viewport that the visitor is actually viewing after scrolling, including themes whose document uses visible overflow.
- Let site owners hide the guidance next to the "Public" button while keeping it visible within the report form.
- Ships provides complete German translations for both de_DE and de_DE_formal.
- Verifies new turnstile credentials before saving and distinguishes between visitor authentication failures and configuration or temporary provider failures.
1.1.2
- Allows site owners to customize the public widget button and a clearly visible guidance notice from Settings -> FeedbackPilot.
- Uses translated privacy-safe defaults when either field is missing, empty, or contains only whitespace, with no migration required for existing installations.
- Sanitizes both settings as plain text, repeats the notice within the form, and adds automated regression coverage.
1.1.1
- Includes html2canvas-pro and the native Altcha fallback in the plugin ZIP file, so FeedbackPilot no longer requires visitor-browser requests to jsDelivr.
- Keeps Cloudflare Turnstile as an optional, admin-enabled spam protection integration.
- Update the privacy/GDPR documentation to reflect the local asset delivery model.
1.1.0
- Adds FeedbackPilot support for WordPress login, lost-password, retrieve-password, and reset-password screens.
- Adds sanitized auth-screen context to generated issues so that reports from login and password reset pages are easy to triage.
- Redacts reset keys, login identifiers, nonces, tokens, and password-like values from auth-screen URLs, console logs, and issue bodies.
- Clears sensitive login/reset form fields from the cloned screenshot document before rendering, without changing the live page.
1.0.5
- Adds a trusted triage filter to generated GitHub issues so that maintainers and LLM agents can validate visitor reports before turning them into code changes.
- Requires that non-implementation outcomes—such as "already shipped," "duplicate," "needs more information," "not planned," "irrelevant," or "spam"—remain explicit options during triage.
- Update the LLM agent guidance and smoke checks for this prompt-injection defense-in-depth layer.
1.0.4
- Makes the visitor-facing widget and modal copy easier to understand for non-technical users; GitHub and issue-tracker terminology is kept out of the front end.
- Localizes the native Altcha fallback challenge UI when the standalone Altcha WordPress plugin is not installed.
- Prevents the browser or password manager's autofill feature from interfering with the Turnstile credential fields on the settings page.
1.0.3
- Displays user-friendly, localized error messages instead of internal REST error codes such as rate_limited.
1.0.2
- Fixes an issue where CAPTCHA-protected submissions were incorrectly triggering the unauthenticated 60-second burst limiter after a solved Altcha or Turnstile challenge.
- Failed or missing CAPTCHA submissions no longer use up a report rate-limit slot; the hourly per-IP limit still applies to successful reports.
1.0.1
- Fixes screenshot capture on pages where CSS `text-transform` changes the text length, preventing an upstream `html2canvas-pro` `Range.setEnd` `IndexSizeError`.
- Documents on Cloudflare Turnstile CSP requirements for sites with strict Content Security Policy headers.
- Adds a simplified browser fixture for the html2canvas text-transform regression.
1.0.0
- First stable release for production use.
- Adds improvements to ensure GDPR compliance: a privacy notice for visitors, admin controls to disable screenshot capture and console log inclusion, and server-side enforcement of those minimization settings.
- Harden Cloudflare Turnstile validation by linking tokens to the expected action and hostname.
- Retains the v0.1.16 security enhancements: native Altcha replay protection, prompt-injection boundaries, proxy-aware rate limiting, AES-256-GCM token storage, and validated screenshot storage.
- Updates to the README, the German README, readme.txt, the wiki privacy guidance, translations, and smoke tests for the v1.0 release.
0.1.16
- Security hardening release: The native Altcha fallback now uses delimited salts, strict validation, expiration checks, and replay protection.
- Prompt injection follow-up: Metadata provided by visitors and console logs are isolated and normalized as untrusted content, with a suspected-injection hook designed to minimize PII for integrations.
- Rate limits now rely solely on REMOTE_ADDR by default, with explicit Cloudflare and generic reverse-proxy modes.
- Token storage now uses a versioned AES-256-GCM envelope where available, with support for legacy AES-256-CBC read and migration operations.
- Screenshot storage now enforces PNG size and pixel limits and re-encodes PNGs using GD when available.
- Turnstile secret placeholders no longer risk overwriting stored secrets; cache flushing now targets only FeedbackPilot's EDD-SL cache key.
0.1.0
- Initial release. Console catcher, annotated screenshot, GitHub-Issue submission via OAuth-connected user token (or manual fine-grained PAT).